Private AI for teams: keep your company's data out of model training
Private AI means your company's documents are kept out of model training, are encrypted, and are visible only to the people you grant access to. To choose one, confirm three things: zero data retention with the model provider, encryption plus per-person access control, and answers that come from your own files rather than opaque web data. Tatsulok sends every chat request only to model providers under zero data retention, encrypts your files at rest, and lets you set access per person.
Updated
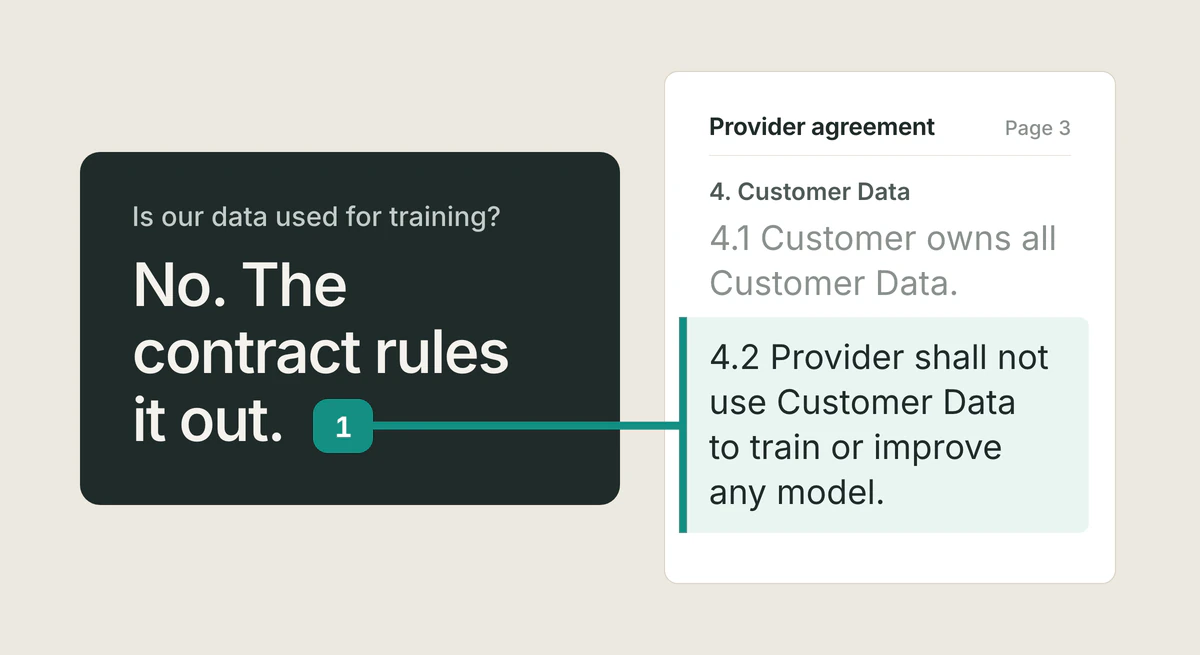
Does AI train on your data?
It depends on the tool. Many consumer AI products may retain prompts and uploaded files and use them to improve or train future models unless you opt out. The risk is that confidential material, contracts, customer records, internal strategy, can be absorbed into a model you do not control and surface elsewhere.
The safe posture is zero data retention with the model provider: the provider processes your request, returns an answer, and keeps nothing for training. Tatsulok sends every chat request only to model providers under zero data retention, so your questions and the passages sent with them are neither kept by those providers nor used for training. Voice input, web search, document extraction and search reranking run under their own providers' terms, listed in our privacy policy.
The privacy worry is widespread and well-founded: Cyberhaven's analysis of workplace AI use found that roughly 11% of what employees paste into ChatGPT is sensitive company data, exactly the kind of leak a private, access-controlled workspace is designed to prevent.
What makes an AI tool private?
Privacy is mechanics, not a slogan. A genuinely private AI tool does three concrete things. First, it guarantees your content is never used for model training. Second, it encrypts your data in transit and at rest, and keeps it private by default rather than shared or public. Third, it gives you real control: you decide who can see each document, per team or per person, and you can delete content at any time.
If a tool cannot describe each of these in plain terms, treat the privacy claim as unverified.
How do teams keep shared documents confidential?
Confidentiality inside a team is an access-control problem. The answer is not to stop sharing, but to share precisely. Each document should have explicit access, granted to a specific team or a specific person, so a file is visible only to those who need it.
When someone leaves a project or the work ends, revoke their access and delete what is no longer needed. In Tatsulok, you control access per team and per person.
Does team knowledge survive when people leave?
Confidential knowledge should outlast the people who created it. When answers live in individuals' private chat histories, that knowledge walks out the door when they do, and you have no way to revoke it.
A private team library fixes this. Because documents live in one access-controlled place rather than scattered prompts, institutional knowledge keeps accumulating, and you can revoke a departing person's access without losing what the team built. Continuity and control are the same mechanism.
How does Tatsulok protect your data?
Tatsulok keeps your data private by default, and your workspace is never sent to training datasets. Your files are encrypted at rest, you control who can access them, per team or per person, and you can delete anything at any time.
Just as important, answers about your files come from your own documents, and each one is cited to the exact source passage, with a highlighted preview and a link back to the original, so you can verify where every statement came from. Tatsulok reads PDF, Word, Excel and PowerPoint files and works in English and Japanese.
FAQ
- Does Tatsulok use my documents to train AI models?
- No. Chat requests go only to model providers under zero data retention, which commit to no training and to keeping none of your content afterwards. Voice input, web search, document extraction and search reranking run under their own providers' terms, listed in our privacy policy.
- Is my data encrypted?
- Yes. Your files and workspace database are encrypted at rest with AES-256, connections use HTTPS, and everything is private by default rather than shared or public.
- Who can see the documents I upload?
- Only the people you grant access to. You control access per team and per person, so each document is visible only to those you choose.
- What happens to team knowledge when someone leaves?
- It stays. Because the knowledge lives in the team's access-controlled shared library rather than in one person's chat history, it remains available to everyone you've granted access. You can revoke the departing person's access while the institutional knowledge keeps accumulating.
- Can I delete my content, and is it really gone?
- Yes. Deleted items go to Trash and are deleted, with their stored copies and search index, after at least 30 days, or at once with Delete Permanently.
- Where do the AI answers come from?
- Answers about your files come from your own uploaded documents. Each is cited to the exact source passage, with a highlighted preview and a link to the original so you can verify it.
Sources
Related guides
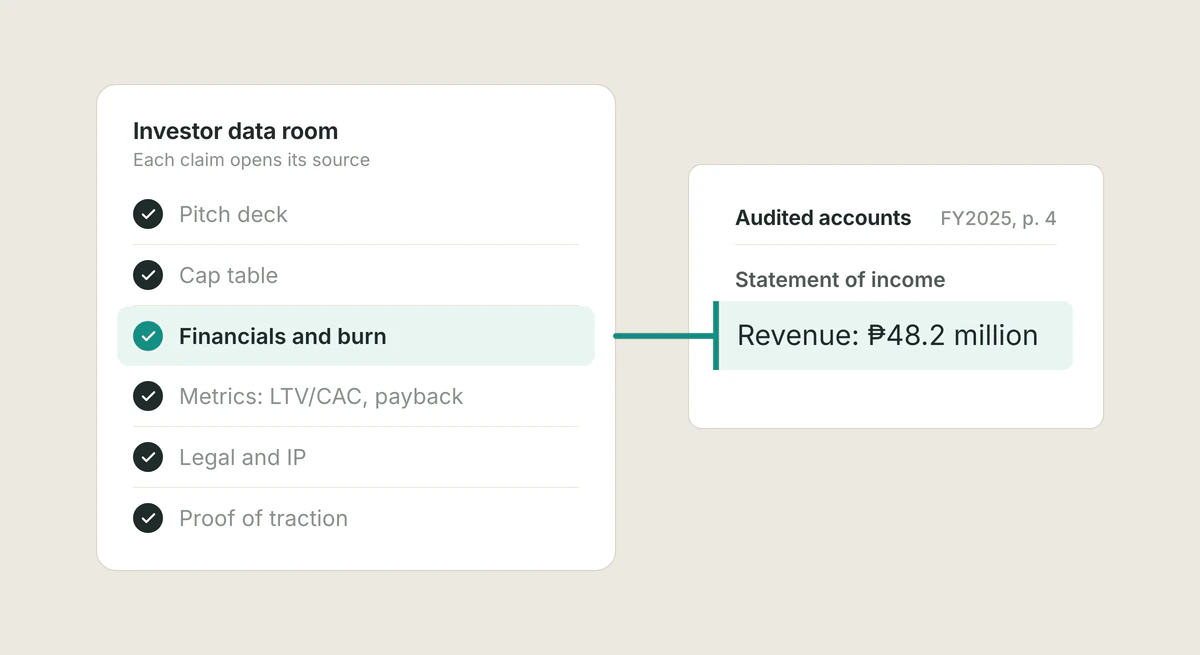
Data room checklist
A startup data room for fundraising should include your pitch deck, cap table, financials, legal documents, and proof of traction, organized so investors can verify every claim. Here is the full checklist.
Read the article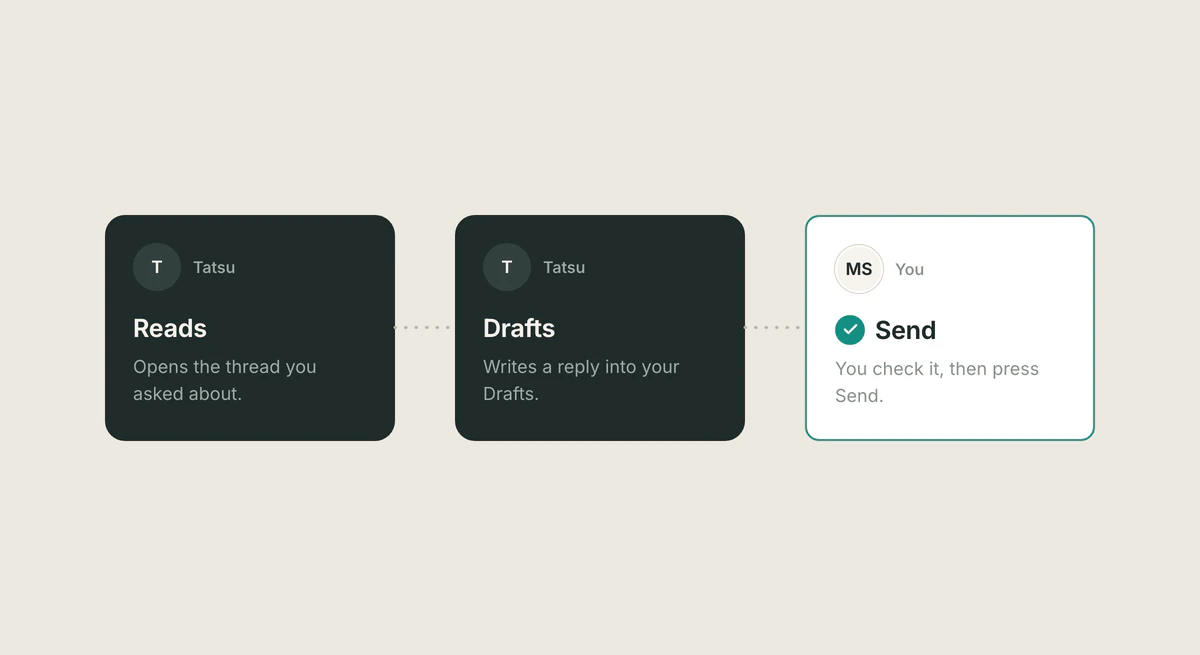
Safe email access
Read, draft and send are three different permissions. What each lets an assistant do in Gmail or Outlook, why sending should stay with you, what Google's unverified-app screen means, and how to remove access.
Read the article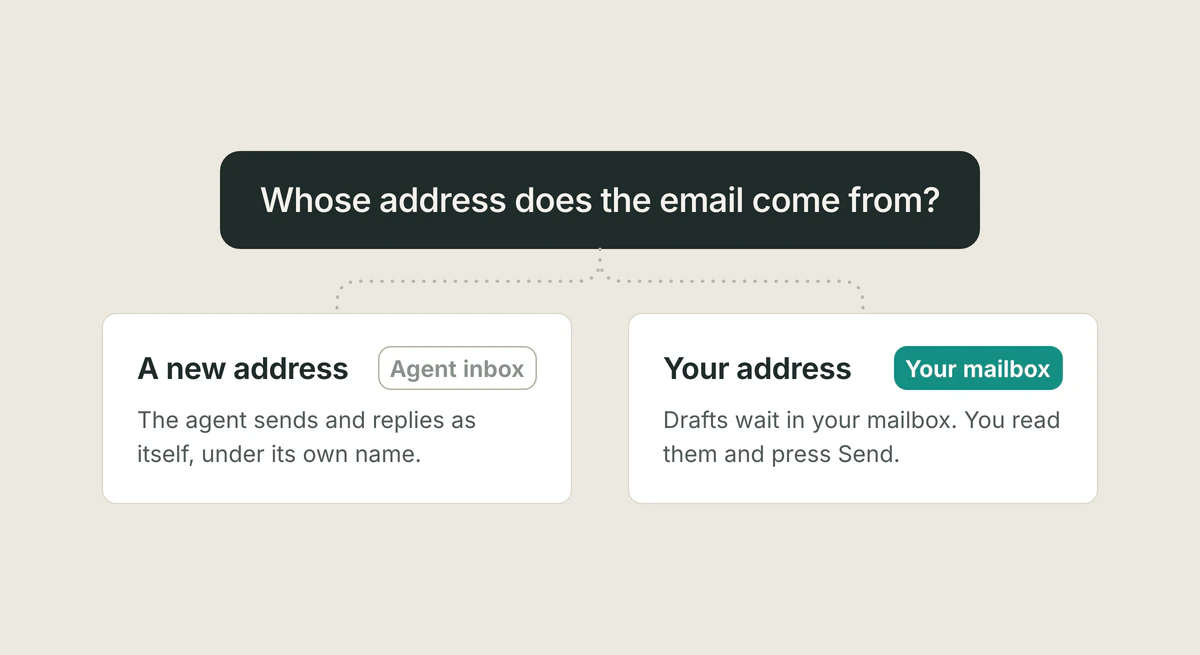
Email for AI agents
If an agent must send and receive mail as itself, give it its own inbox. If you want help with your own mail, use a tool that drafts in your mailbox and leaves Send to you. Where MCP servers fit, checked 14 October 2026.
Read the article